ZDNET’s key takeaways
- Okta, AWS, Google Cloud, Salesforce, and others kind an AI agent safety coalition.
- The Alliance affords a blueprint for corporations searching for visibility, management, and governance of brokers.
- AI brokers want the equal of a kill swap to expeditiously terminate suspicious conduct.
When a swarm of AI brokers, many autonomously provisioned by different poorly ruled AI brokers, escaped OpenAI’s labs and stole info from servers belonging to a different firm (Hugging Face), many specialists seen the incident as a significant tipping level in cybersecurity and AI cyber capabilities. (To what extent are fashions now resourceful sufficient to have interaction in self-directed hurt?)
OpenAI referred to the incident as “unprecedented.” It was the primary AI-directed assault of its nature to go viral throughout mainstream headlines, and it wasn’t lengthy earlier than stories of different agents-gone-wild made headlines as properly. The latest of those stories concerned three corporations that have been inadvertently attacked by Google Gemini agents.
Additionally: Who’s responsible for catching rogue AI agents? You are
Important controversy has ensued.
In a single nook are the inventors of AI themselves, saying that the time has come to take a breather from AI innovation to be able to get the expertise underneath management. You’d assume they need to know. For instance, OpenAI sounded the alarm that a swarm of potentially malicious AI agents is just months away from wreaking havoc.
Within the reverse nook is US President Trump posting to his Fact Social community that “AI taking on the World, destroying Humanity, and all different issues unhealthy, is a HOAX.”
In between are all the companies and customers getting whipsawed between the 2 factors of view and attempting to determine what to do subsequent.
(Disclosure: Ziff Davis, ZDNET’s dad or mum firm, filed an April 2025 lawsuit in opposition to OpenAI, alleging it infringed Ziff Davis copyrights in coaching and working its AI techniques.)
Additionally: ‘Sophisticated’ AI swarm attacks are months away, OpenAI warns
Two huge questions are arising out of this dialog. First, what will be performed over the quick and long run to get the expertise underneath management? Second, how can defenders greatest allow themselves for quick intervention as soon as suspicious exercise is detected?
With the objective of serving to companies reply these two questions and to set the stage for world-class governance and administration of their agentic estates, a number of corporations, together with Okta, Google, Amazon Internet Companies (AWS), and Salesforce, have joined forces to kind the Blueprint Alliance.
The Alliance was introduced this week at Okta’s annual Oktane convention.
4 questions each enterprise should reply
In its first blueprint for agentic visibility, management, and governance, the Alliance centered on 4 questions that each one companies ought to be capable of reply for themselves:
- The place are my brokers?
- What can they do?
- What are they doing?
- How do I reply?
In accordance with recent research performed by LastPass (not a member of the Alliance), 92% of enterprise admins say AI is already in use throughout their group, however solely 27% have an enforced AI governance program. Okta’s analysis stories related statistics, discovering that 92% of organizations use autonomous brokers, however solely 34% safe these brokers with the identical rigor as people.
In the meantime, Gartner’s research paints an excellent bleaker image, discovering that solely 13% of organizations imagine they’ve the best AI agent governance in place. In different phrases, most organizations in all probability don’t know the reply to some or the entire above questions. The fourth query is especially essential due to the diploma to which problematic brokers working at machine pace have shortened the response window.
Additionally: AI just broke your career ladder – here are 6 new ways to the top
As Picus Safety affiliate safety analysis engineer Umut Bayram instructed ZDNET, “Within the AI period, organizations can’t reply to assaults that unfold in minutes with processes that take days. Attackers are already working at machine pace, and safety groups want to have the ability to reply at that tempo.”
In equity, not all anomalous agent exercise is malicious. Right here’s one other state of affairs that calls for an instantaneous response: a well-intentioned agent enters an infinite loop, leading to extreme billing for LLM entry. At machine speeds, such a loop may burn by a whole group’s AI price range within the blink of a watch. The earlier such an agent is disabled, the higher for the underside line.
The most effective defenses are scenario-specific
After all, within the cybersecurity world, pace has at all times been important — however by no means extra so than now. And given how defenders might solely have minutes or seconds to reply as soon as they’ve been alerted to anomalous agent exercise, what ought to be their weapon of selection?
To be clear: There isn’t any silver bullet. As with all cybersecurity, one of the best defenses are scenario-specific and can contain layers of precautionary measures, some that concentrate on visibility into agentic actions, and others that tune the safety postures of our computer systems and networks to rising agentic behaviors and patterns.
Additionally: Even an AI cost-management vendor can lose control of its agent spending
For instance, companies should be ready to defend in opposition to malicious brokers of unknown origin in addition to internally provisioned brokers that, for no matter causes, stray from their mandates. Not like robotic automations that ship extremely deterministic outcomes (they do precisely as they have been programmed to do), brokers are probabilistic to the extent that their underlying fashions afford them the company to take issues into their very own palms.
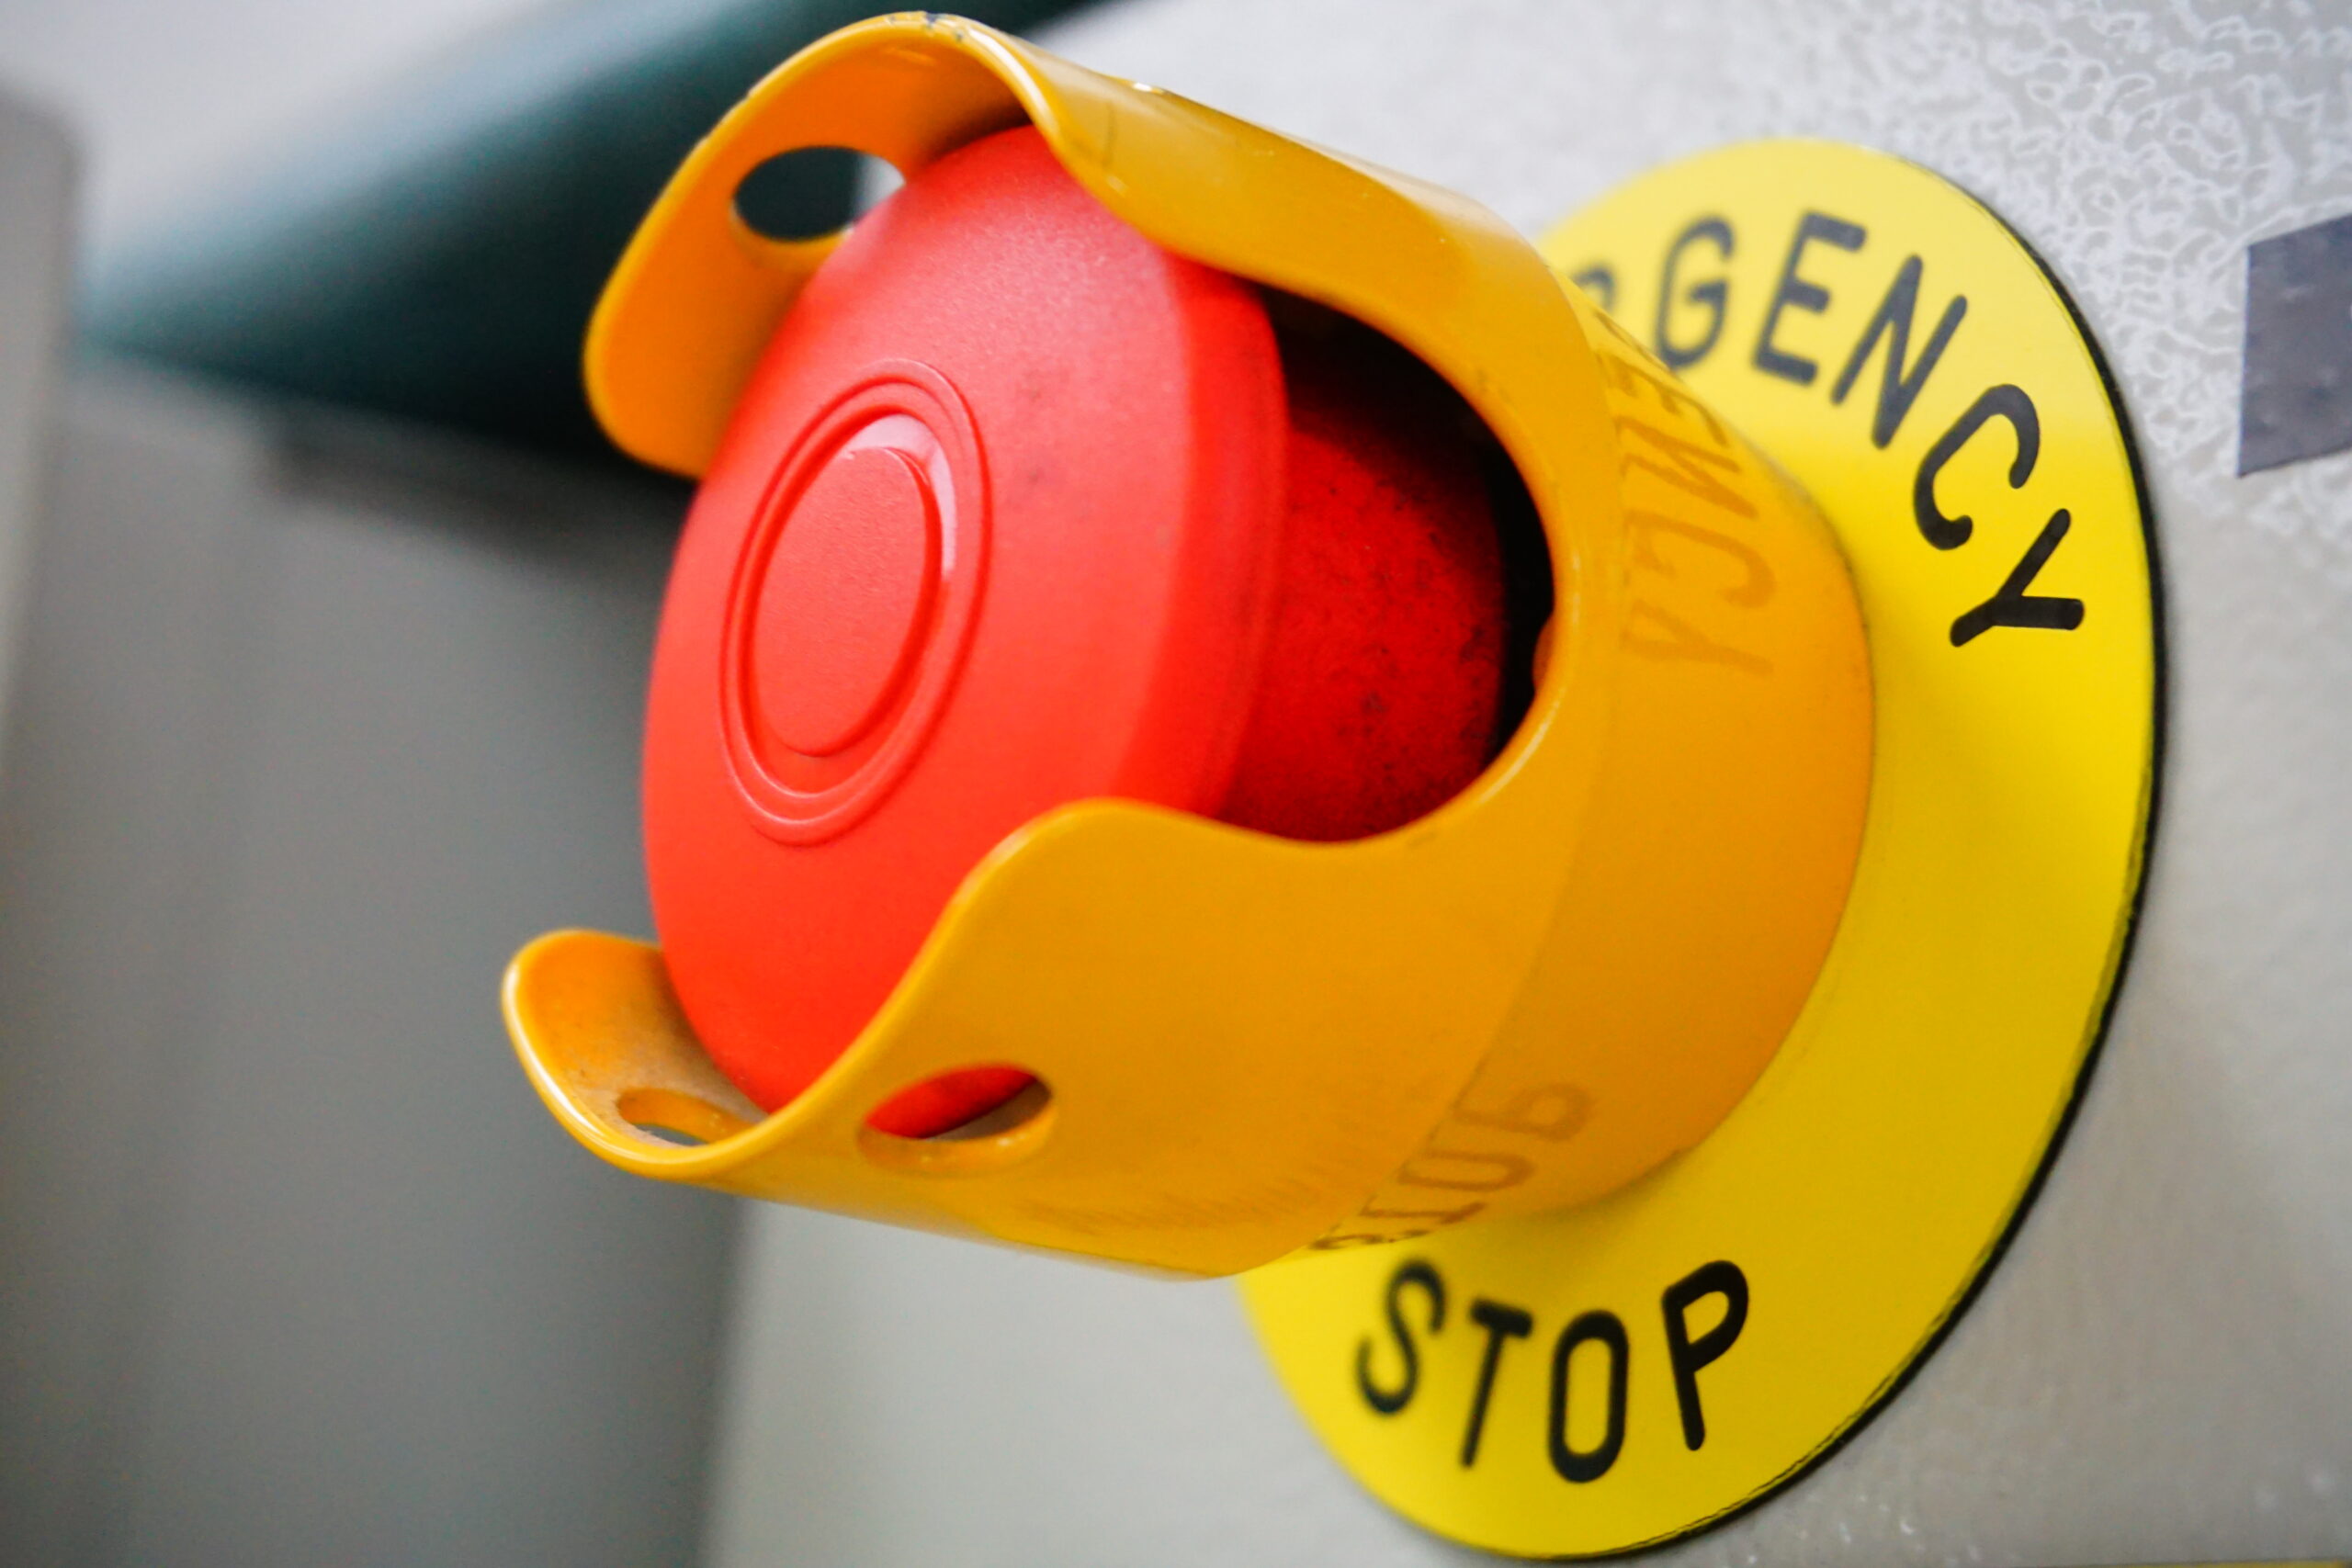
When mere seconds could make the distinction between the life and loss of life of your techniques and even your enterprise, the best weapon of selection could be some kind of kill swap — one thing like the massive purple button on an escalator. When unsure, neutralize the agent first, ask questions later.
What’s a kill swap?
In an effort to place organizations on the best path, the brand new alliance revealed six operational rules, one in all which states that “each agent wants an instantaneous kill swap to droop or terminate operations, with a transparent path to revive operate.” However, virtually talking, what precisely is a kill swap, and who might need entry to at least one?
It relies upon.
For instance, within the case of OpenAI’s assault on Hugging Face, the brokers belonged to OpenAI. Presumably, if OpenAI had the best governance controls in place (it didn’t), it might need detected that its personal brokers have been participating in suspicious conduct, after which somebody at OpenAI with entry to a kill swap may have pulled the plug. What about Hugging Face? Did it have entry to a kill swap? Most likely to not the extent that OpenAI did, because it was OpenAI’s brokers that led the assault. However what if an assault on a sufferer like Hugging Face concerned the theft of its credentials to some on-line service or enterprise utility?
Additionally: Nearly 70% of workers use AI regularly now – but many get no time to upskill
As we speak, one of many extra coveted credentials that cybercriminals wish to steal are OAuth tokens. These are a kind of credential that provides one utility (e.g. Slack) entry rights to learn and replace one other utility (e.g. Google Drive) on behalf of a particular consumer. In that context, the Google-issued OAuth token that provides Slack the entry it must work with a particular consumer’s Google Drive is actually a proxy for the consumer’s Google ID and password.
In a state of affairs that entails an agent (pleasant or malicious) utilizing an OAuth credential (stolen or not) to work together with a delicate useful resource, a neutralization of that token (referred to as “token revocation”) would primarily quantity to a kill swap.
In different phrases, for sure forms of assaults, the sufferer might need a kill swap at their disposal. And that very same choice applies to the group’s personal brokers as a result of, in the event that they’re doing it proper, then their very own brokers are additionally utilizing OAuth tokens to entry all of their techniques of document to be able to do what brokers do greatest (autonomously full duties that usually require entry to a number of techniques).
The position of OAuth tokens
With regards to granting one utility entry to a different, customers are already conversant in the everyday OAuth expertise (although they could not comprehend it’s technically known as an OAuth workflow). In earlier days, customers would enter their Gmail consumer IDs and passwords straight into Apple Mail or Outlook to ship and obtain electronic mail by their most popular electronic mail consumer. As we speak, nevertheless, Google affords a safer various that depends on OAuth tokens. As an alternative of supplying your Gmail consumer ID and password to a third-party electronic mail consumer like Apple Mail in your iPhone (a extremely insecure follow), Gmail pops up a consent dialog that, as soon as accepted by the consumer, grants a Gmail entry token to their electronic mail consumer. From that time on, the e-mail consumer ought to be capable of ship and obtain emails with out requiring repeated grant requests.
Nonetheless, ought to the consumer lose their iPhone and, as an additional precaution, need to revoke that token, the method is a little more sophisticated: it requires a go to to a Google internet web page the place customers can handle tokens they’ve already issued.
Additionally: Why Microsoft won’t send you SMS texts for login anymore
As customers begin to deploy brokers that work together with the entire companies they use (Gmail, Google Drive, Amazon purchasing, social media, music streaming, and so on.), they don’t seem to be solely more likely to encounter many extra Oauth workflows, however they might want to familiarize themselves with every service’s token revocation course of as a matter of their private operational safety practices.
For companies, nevertheless, particularly ones that depend on an identification administration resolution like these provided by Okta, Microsoft, and Ping, those self same tokens ought to be managed in a means that centralize token issuance and administration right into a single system the place it’s the IT managers who not solely have entry to the proverbial kill switches (the ability to revoke any token that’s related to any human or agentic-powered integration), but additionally, in reply to the “The place are my brokers?” query, provide visibility and management over the group’s complete agentic property.
Nonetheless, to facilitate these kill switches and that centralized visibility and management, a brand new extension to the underlying OAuth customary was wanted, permitting the central IdP (identification supplier) to take duty for OAuth workflows and administration when AI brokers are concerned. It was simply on this previous 12 months that the open customary agentic-sensitive extension –referred to as the IETF’s Id Assertion Authorization Grant (IAAG) — fell into place, thanks largely to the work performed by Okta director of identification requirements Aaron Parecki.
Implementing the usual
Nevertheless it’s one factor for folks like Parecki and others, together with IAAG co-author Brian Campbell (Ping Id), to writer a brand new customary and to attain customary consensus on the Web Engineering Activity Drive. It’s one other for that customary to be baked into the assorted IdPs in a means that facilitates the supply of a readily accessible kill swap within the occasion that the reply to the third query is “one thing they shouldn’t be doing.”
On the Oktane convention, Okta executives gave prospects an illustration of how its identification and safety options depend on the brand new customary to supply IT managers and CISOs with visualizations that, along with answering the 4 questions, additionally empower them (and even an agent engaged on their behalf) to take motion.
Additionally: Don’t let an AI chatbot pick your password, ever
For instance, the screenshot under depicts how a single Claude-based agent has been afforded entry to Slack, Salesforce, Atlassian, and GitHub by two separate agent gateways.

Beneath the hood, OAuth isn’t simply giving Claude entry to these functions. It’s additionally controlling the diploma of entry, an essential nuance to the thought of a kill swap. For instance, a kill swap that absolutely revokes a token would primarily deprovision an agent’s entry to a back-end utility resembling Salesforce. However one other sort of kill swap may merely revoke sure permissions to work together with Salesforce.
Deprovisioning demonstration
“There are literally two eventualities right here,” Okta chief product officer Ely Kahn instructed ZDNET. “There’s the one the place your individual brokers begin to exhibit bizarre conduct, and it’s a must to kill them [the nuclear option] simply to cease that conduct earlier than it will get uncontrolled. However then there’s one other state of affairs the place you possibly can simply put a brand new guardrail in place. For instance, a brand new guardrail that forestalls the exfiltration of sure knowledge or only a change within the permissions afforded to the agent.”
Throughout Okta CEO Todd McKinnon’s convention keynote, Oktane attendees obtained a glimpse of what that deprovisioning appears like in follow. As quickly as a Claude agent was requested to ahead confidential info from Salesforce to an worker’s private electronic mail deal with, one other agent detected the prohibited conduct, deprovisioned the primary agent’s entry to Salesforce (revoked its token), notified the agent’s human proprietor that Salesforce entry was now denied, and despatched a message by way of Slack to the IT division together with any particulars that might be helpful when it comes to a treatment or restoration of entry.
Additionally: Your AI vendor could land you in legal hot water
Talking to the necessity for pace described by Picus Safety’s Bayram, your entire course of was accomplished in a matter of seconds, lengthy earlier than any human may have assembled a response.
In his keynote, McKinnon additionally identified that IdPs like Okta can’t essentially deal with each facet of the Blueprint Alliance’s blueprint and that among the non-identity-based telemetry that helps to find out what an agent is doing should come from different sources. That mentioned, Okta additionally confirmed two different instruments that might be useful to companies trying to achieve management of their agentic property. One in every of these — Shadow AI Agent Discovery for Endpoints — helps organizations uncover unsanctioned “shadow” AI brokers roaming firm networks.
One other instrument — Okta Id Risk Safety — aggregates threat intelligence from different agentic threat detection options (CrowdStrike, Zscaler, SentinelOne, Palo Alto Networks, and so on.) right into a single view for human- or agentically pushed remediation selections.